Digital Forensics
Connect the account records to the event.
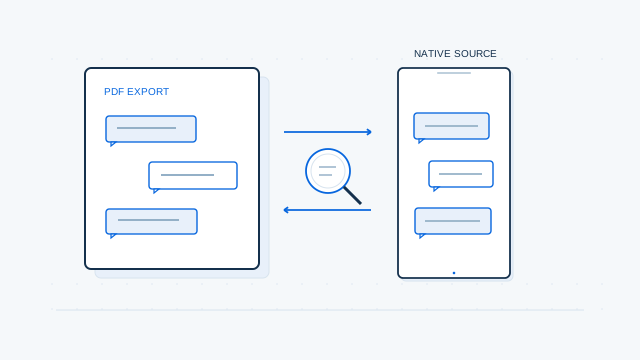
Preserve and examine relevant mailbox, attachment and cloud activity records from authorized accounts.
01
Define accounts, dates and permissions.
Start with the relevant users, services and time period. Identify who can authorize access and whether an administrator or account owner needs to assist. A mailbox collection and an audit-log collection are different parts of the evidence picture.
02
Preserve the useful context.
Consider relevant message content, attachments, headers and available activity records. The purpose is to help answer the instructed questions, not to gather unrelated business information without a reason.
03
Report available evidence, not assumed history.
Account records vary by platform and configuration. Microsoft’s audit guidance shows why retention and licensing need to be checked for the actual environment. Missing logs should be documented as a limitation, not treated as proof that nothing happened.
RELEVANT SOURCES
Start with what is available.
Discuss the sources that can help answer the question, within an authorized scope.
 Microsoft 365 and authorized mailboxes
BEFORE WE BEGIN
A more useful first conversation.
- Identify the accounts and administrators.
- Describe retention or licensing information if known.
- Discuss a secure authorized access method.
RELATED ARTICLES
Useful before you need us.
Practical perspectives and clear next steps.
YOUR NEXT STEP
What do you need to understand?
Tell us what you need to understand.