

Assess
We establish what is known with your team and agree the immediate priorities.
SERVICES / INCIDENT RESPONSE
If ransomware, business email compromise, or data theft disrupts your organization, we help you understand what happened and coordinate the next decisions with your response team.
STRUCTURE UNDER PRESSURE
We clarify the situation with your team.
We coordinate actions with your IT team.
We examine the available evidence.
We help you make informed recovery decisions.
WHEN TO BRING US IN
We bring specialist investigation and coordination support to the situation your team is facing.
Incident Response
When ransomware disrupts your organization, we help you establish what is known, investigate the evidence, and coordinate response priorities with your team.
ExploreIncident Response
If a suspicious email, account event, or payment request raises concern, we help you investigate what happened. We examine relevant communications and available account records to support a coordinated response.
ExploreIncident Response
We help you understand the evidence of unauthorized activity and possible information exposure. Our investigation gives your response team a clearer basis for assessing affected systems, accounts, and information.
ExploreINVESTIGATE / COORDINATE / EXPLAIN
We agree the scope, explain our findings, and keep responsibilities clear so your team can act on the evidence.
Incident Response
We turn available technical records into a clearer account of what happened during your incident. You receive findings tied to the evidence, with the remaining uncertainty explained.
ExploreIncident Response
We help your team move from incident findings to coordinated recovery decisions and practical improvements. We keep unresolved questions and responsibilities visible as operations resume.
ExploreIncident Response
You do not need a complete account of the incident before contacting us. We start with what you know, discuss the help you need, and clarify scope, availability, and responsibilities before work begins.
ExploreIncident Response
We help your team preserve relevant evidence while coordinating containment and recovery. We identify sources that may change or disappear and plan collection around the realities of the incident.
ExploreOUR RESPONSE
We adapt the sequence and priorities to your incident. Investigation, containment, and recovery may need to progress together.
We establish what is known with your team and agree the immediate priorities.
We coordinate containment decisions with the team responsible for your systems.
We examine the relevant sources and explain the findings and their limits.
We help your team connect the findings to recovery decisions and practical improvements.
YOUR TEAM AND OUR EXPERTISE
We work alongside your existing IT provider and advisers, with each person’s responsibilities agreed rather than assumed.
We combine your team’s knowledge of the environment with specialist forensic investigation.
ExploreWe help you connect business priorities and decision authority to a coordinated response.
ExploreWe provide scoped technical findings so you can advise the organization with the evidence in view.
Explore
When authority is unclear and decisions have not been rehearsed, disruption can continue while costs and customer commitments build. Through BreachReady, we lead your preparation: building the plan, practicing decisions with your team, and guiding improvements, with specialist support agreed in advance.
YOUR READINESS JOURNEY
We assess your starting point with you.
We build your plan and clarify responsibilities.
We rehearse the decisions with your team.
We guide follow-through as your needs change.
RELATED ARTICLES
We share the questions and methods that can help you make a more informed next decision.
Article
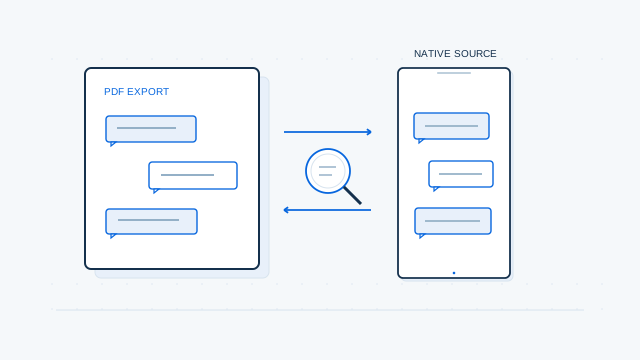
If a message exhibit is disputed, we help you identify what needs to be tested and compare it with lawfully available source records. We explain what can be established and where the evidence falls short when devices or accounts are unavailable.
Read article
Article
We help you plan the preservation and examination of mobile conversations, from SMS, MMS and iMessage to WhatsApp, WeChat, Telegram and Signal. The right approach depends on your devices, accounts and available records; no method can promise access to every device or backup.
Read article
Article
When you suspect employee data theft, you need to protect the business without losing the evidence. We explain how to coordinate offboarding, lawful collection, cloud logs and device evidence while keeping allegations separate from verified facts.
Read articleYOUR NEXT STEP
Tell us what you know so far. We will discuss the support you need and the next step.


